
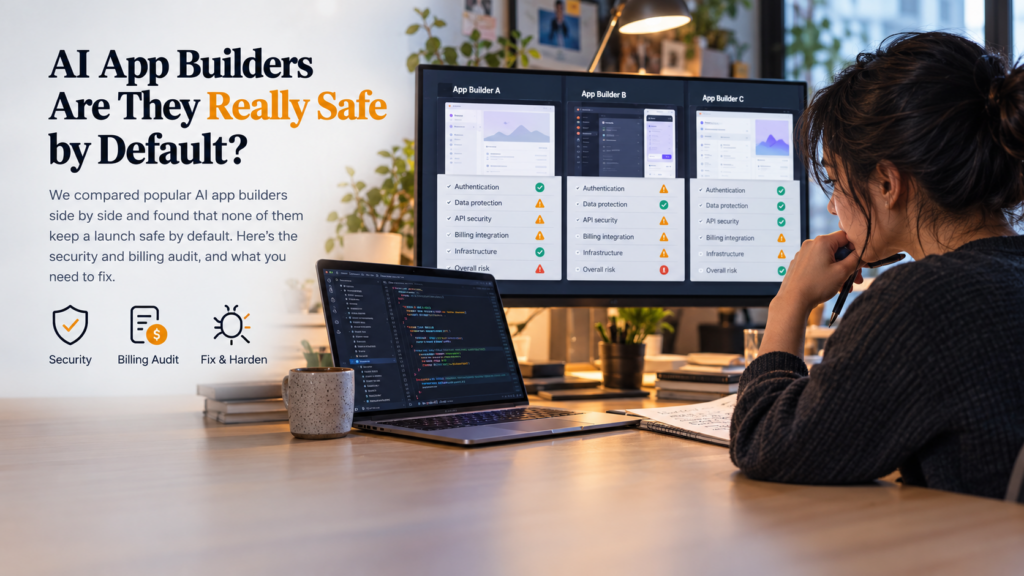
Founders ask us the same question every week: when you put lovable vs replit vs base44 security compared side by side, which one actually keeps a launch safe? The honest answer is none of them, by default — every platform leaves real gaps that only get closed through manual hardening. This guide puts the table first, then walks through why each platform earns its grade.
Quick Comparison Table: Lovable vs Replit vs Base44 Security
Here is the condensed verdict before the detailed reasoning. Each row reflects documented incidents and default configurations, not marketing claims.
- Lovable: Fast Supabase scaffolding, but Row Level Security is the gap most often flagged in independent security write-ups — the most documented RLS risk of the three.
- Replit: Broadest infrastructure surface area (hosting, auth, database, deployment) means more configuration footguns, even though the platform itself has solid baseline tooling.
- Base44: Tighter review since the Wix acquisition, but still inherits the same AI-generation risk patterns as its competitors — no platform is exempt.
- All three: Billing and webhook handling is a separate, equally costly risk category that platform choice does not solve.
If you only remember one thing from this lovable vs replit vs base44 security compared breakdown, make it this: platform choice is a starting point, not a security guarantee.
Lovable Overview
What Lovable is built for
Lovable is designed for conversational, rapid app generation — describe a product and get a working Supabase-backed app in minutes. That speed is the entire pitch, and it’s genuinely useful for prototyping. The tradeoff is that the generated backend often ships with permissive defaults, because the priority is getting something running, not getting something locked down.
Known security incidents and RLS gaps
Row Level Security — the Postgres feature that restricts which rows a user can read or write — is the gap most often named in Lovable security coverage. Security researchers have reported Lovable-generated apps with RLS disabled or scoped so loosely that any authenticated user could query other users’ data. We haven’t run a controlled audit of our own client migrations to confirm a specific rate, so take this as a documented risk pattern rather than a measured one — it mirrors wider findings across the Supabase ecosystem, which we cover below.
Replit Overview
What Replit is built for
Replit covers a wider slice of the stack — code editor, hosting, database, and deployment in one environment. That breadth is attractive for founders who want fewer vendors to manage, but it also means more surfaces where a misconfiguration can slip through: environment variables, auth tokens, and database rules all live in the same project.
Documented auth and data exposure issues
Independent research has repeatedly flagged AI-generated apps — regardless of host — for inverted or client-side-only authentication, where the check that should happen on a server happens in the browser instead and can be bypassed by anyone who opens developer tools. Security firm RedAccess, as reported by Axios, found roughly 380,000 publicly accessible apps built with Lovable, Replit, Base44, and Netlify, including about 5,000 containing sensitive corporate data. Replit’s CEO disputed the framing, saying a public app is “expected behavior” that users can change at any time, and that researchers gave the company only 24 hours’ notice before publishing. Either way, the exposure wasn’t unique to Replit — it turned up across every platform RedAccess checked.
Base44 Overview
What Base44 is built for
Base44 targets non-technical founders who want a complete app — frontend, backend, and database — generated from a prompt with minimal manual setup. It’s closer to Lovable in audience than to Replit, which leans more toward developers comfortable editing raw code.
Security track record since Wix acquisition
Since Wix acquired Base44, review processes around generated apps have reportedly tightened, which is a positive signal for founders weighing lovable vs replit vs base44 security compared as a launch decision. But tighter review doesn’t eliminate the underlying risk: Base44 apps are still AI-generated from the same category of models that produce missing RLS policies and unverified payment integrations elsewhere.
Feature-by-Feature Breakdown
Row Level Security defaults
None of the three platforms turns on strict RLS automatically. FlutterFlow, a comparable builder outside this specific trio, runs into a similar trap one step removed: when a new FlutterFlow project connects to Firestore, it’s Firebase’s own default rules — not something FlutterFlow generates — that leave the database open to any request, authenticated or not, until a hardcoded 30-day expiration date. FlutterFlow doesn’t override that default, so the same open window applies unless someone replaces the rules, and most non-technical builders never notice until it’s too late.
Authentication implementation patterns
A pattern that shows up across AI-generated SaaS products: auth checks exist only in the frontend, with no server-side verification, so a Stripe “integration” can turn out to be a button wired to nothing. A specific version of this story — a YC-backed startup, a six-week fix, $40,000 billed against a $150,000 agency quote — circulates in vibe-coding commentary, but we couldn’t verify those figures against a public source, so treat them as illustrative of the failure mode rather than a documented case. The underlying pattern — frontend-only auth, a payment button with nothing behind it — is well documented even where this particular anecdote isn’t.
Payment and webhook handling
Billing failures are platform-agnostic and often invisible for months. A Stripe webhook that silently returns “200 OK” without actually revoking access from a failed-payment customer can leave that account active indefinitely — Stripe’s webhook docs confirm a 2xx response is logged as successful delivery no matter what the handler actually did. A specific figure, around $25,300 lost over 11 months, gets attached to this scenario in more than one piece we’ve reviewed on this topic, always without a cited source — we flag that pattern rather than repeat the number as fact. In a separate, better-documented case, GetDevDone’s own write-up describes rebuilding a broken AI-generated payment integration that had silently blocked revenue for about a month before anyone noticed — the opposite failure mode, but equally costly.
Database exposure and the Supabase 98% finding
Security vendor Symbiotic Security scanned 1,072 apps built on Supabase and found that 98% had at least one security flaw, with about 16% flagged for anonymous delete access. That’s a vendor-run scan rather than an independent academic study, and it doesn’t single out Lovable, Replit, or Base44 — it describes the broader category of Supabase-backed apps, echoing the cross-platform pattern RedAccess found above. Any thorough lovable vs replit vs base44 security compared analysis has to treat this as a shared, not isolated, risk.
Monitoring, logging, and breach detection
Stories circulate of a Cursor-built SaaS whose paywall was bypassed and billing quota drained within 48 hours of a viral launch, forcing a shutdown within a week — we couldn’t confirm the product or the figures against a public source, so we’re not naming one here. The underlying risk is real regardless of whether that particular story checks out: none of the three platforms in this comparison ship meaningful breach-detection alerting out of the box, so that layer has to be added separately, no matter which one you pick.
Pricing
Entry-level plans vs hidden hardening costs
Entry-level plans across Lovable, Replit, and Base44 look similar — affordable monthly tiers aimed at solo builders. What rarely appears on the pricing page is the cost of fixing what the generator left behind: missing RLS, unverified webhooks, and client-side-only auth checks. Those fixes don’t show up until a breach, a chargeback spike, or a silent revenue leak forces the issue.
The $200/month tool to $50,000 agency rebuild gap
This is where the real pricing story sits, even without a single documented case to point to: a founder paying around $200 a month for a vibe-coding tool has two realistic options when something breaks — muddle through alone, or pay an agency on the order of $50,000 for a full rebuild. SuperApps Vibe Coding Fixes exists specifically to fill that middle ground with a fixed-price hardening pass instead of an open-ended agency engagement.
Who Should Use Which
Solo founders prototyping vs production launches
For a weekend prototype with no real users or payment data, the differences in lovable vs replit vs base44 security compared matter less — pick whichever moves fastest for you. The moment you take payments or store real user data, treat every platform the same way: assume RLS is off, assume auth is client-side only, and verify both before launch.
Teams needing compliance-grade auth
Teams handling regulated data — health records, financial accounts, anything touching GDPR or similar frameworks — shouldn’t rely on any of these three platforms’ defaults. Our related breakdowns on billing code review practices and whether a generator can handle accounting-grade software go deeper into what compliance-level scrutiny actually requires.
Verdict
Clear signal on safest default
If forced to rank them, Base44’s tighter post-acquisition review gives it a slight edge, Replit’s broader surface area gives it the most footguns, and Lovable sits in the middle with its well-documented RLS blind spot. But these are differences of degree, not of kind — all three require the same hardening checklist before a public launch.
Why every platform still needs a security audit before scaling
The 98% vulnerability rate found across scanned Supabase apps should settle any argument about which platform is “safe.” None are, without a dedicated hardening pass. If you’re weighing options after reading this lovable vs replit vs base44 security compared breakdown, the next step isn’t switching platforms — it’s auditing whatever you’ve already built, the same way our builder review series approaches other AI app generators.
Still deciding? We can help. Get your free guide — delivered instantly.
Grab the free guide and put these ideas to work right away.
Get new posts by email
Pick the topics you care about — we only email you when something new is published in them.